CSV vs. CSA in Life Sciences: Key Differences and a Practical Transition Guide
Explore the differences between CSV and CSA including their risk-based approaches, testing strategies,applications in regulated pharmaceutical environments.
CSV vs. CSA in Life Sciences: Key Differences and a Practical Transition Guide Life sciences organizations depend on computerized systems to manage manufacturing, laboratory, quality, clinical, regulatory, and validation activities. These systems must perform reliably because a software failure or incorrect record could affect product quality, patient safety, or data integrity.
For many years, Computerized System Validation (CSV) has been the standard framework for demonstrating that GxP systems are fit for their intended use. More recently, Computer Software Assurance (CSA) has gained attention as a more explicitly risk-based and critical-thinking-driven approach.
The discussion around CSV vs. CSA is sometimes presented as a choice between an outdated method and a completely new one. In practice, the relationship is more nuanced. CSA does not remove the need to demonstrate that software performs as intended. Instead, it encourages organizations to focus assurance activities on the areas that create the greatest risk.
What Is Computerized System Validation? Computerized System Validation is the documented process of establishing evidence that a computerized system consistently performs according to its intended use and predefined requirements.
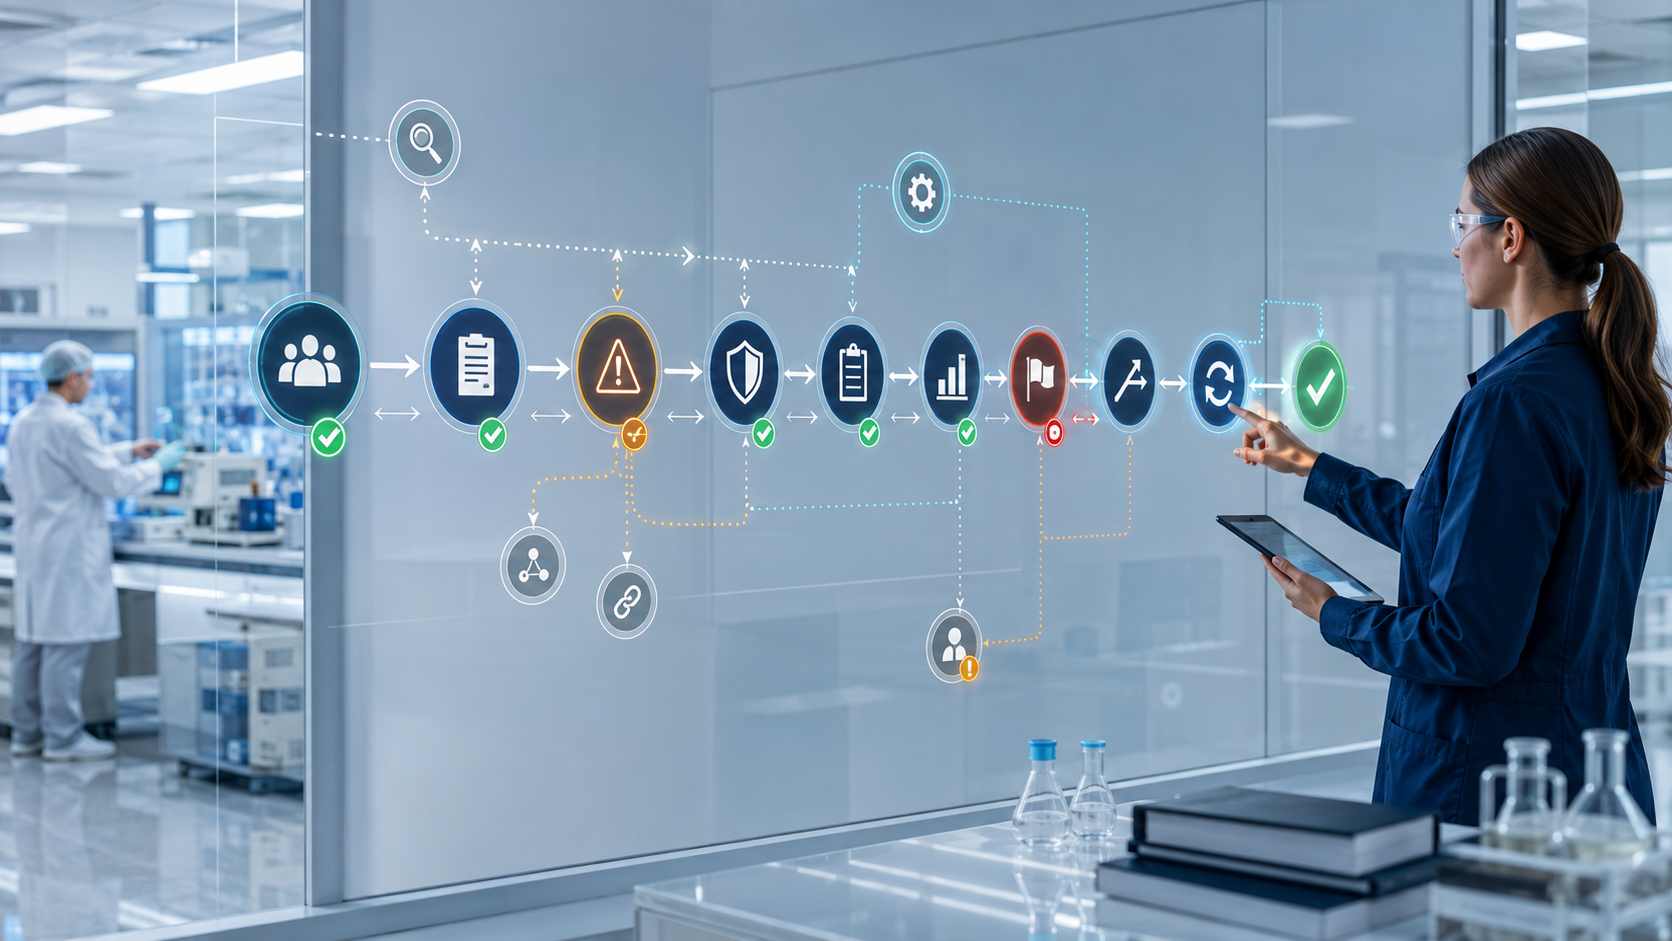
A traditional CSV lifecycle may include:
Validation planning Intended-use definition User requirements Functional or configuration specifications Risk assessments Supplier assessments Installation qualification Operational qualification Performance qualification Requirements traceability Deviation management Validation summary reporting Change control Periodic review System retirement CSV remains an important discipline for regulated pharmaceutical, biotechnology, and medical device organizations. The problem is not validation itself but the way validation is sometimes implemented.
When teams focus on producing documents rather than understanding risk, CSV can become slow, repetitive, and difficult to maintain.
What Is Computer Software Assurance? Computer Software Assurance is a risk-based approach used to establish confidence that software performs as intended.
CSA emphasizes:
Critical thinking Intended use Patient and product risk Appropriate assurance activities Unscripted testing where suitable Efficient use of supplier evidence Capturing sufficient objective evidence Reducing unnecessary documentation Focusing effort on high-risk functions The FDA’s Computer Software Assurance guidance addresses software used in medical device production and quality management systems. Although its formal scope is specific, its risk-based concepts have influenced wider life sciences discussions about modern software assurance.
Organizations should therefore avoid assuming that FDA’s CSA guidance automatically applies in exactly the same way to every pharmaceutical system. Applicable regulations, intended use, GxP impact, and company procedures must still be evaluated.
CSV vs. CSA: What Is the Main Difference? The central difference is not whether software must be tested. Both approaches require sufficient confidence that a system works as intended.
The difference lies in how assurance activities are selected, performed, and documented.
Area
Traditional CSV Practice
CSA Approach
Primary focus
Documented validation evidence
Confidence in intended performance
Decision model
Procedure and deliverable driven
Risk and critical-thinking driven
Testing
Frequently scripted in detail
Scripted or unscripted according to risk
Documentation
Extensive formal records
Sufficient objective evidence
Low-risk functions
May receive similar attention to critical functions
Receive proportionate assurance
Supplier evidence
Sometimes repeated internally
Used when credible and appropriate
Tester behavior
Follows predefined steps
Explores intended use and potential failure
Automation
May be treated cautiously
Encouraged when risk is controlled
Quality involvement
Reviews documentation
Supports risk decisions and assurance strategy
Desired outcome
Approved validation package
Reliable software and demonstrated control
CSA is not “validation without documentation.” It is an approach that seeks to eliminate documentation that does not meaningfully increase confidence or reduce risk.
Does CSA Replace CSV? CSA should not automatically be described as a universal replacement for CSV.
Computerized System Validation remains the broader lifecycle discipline used by many life sciences organizations to demonstrate that systems are suitable for their intended use. CSA provides a practical method for making software assurance more efficient and risk-based.
A mature organization may retain its validation lifecycle while applying CSA principles to:
Determine the level of testing Select scripted or unscripted test methods Use supplier evidence Prioritize high-risk functions Reduce unnecessary screenshots Improve testing efficiency Automate repeatable tests Capture evidence in a structured system In this model, CSV defines the controlled lifecycle while CSA improves how assurance activities are planned and executed.
The Role of Intended Use Intended use is the foundation of both CSV and CSA.
Before determining the validation or assurance approach, the organization should understand:
What the software will do Which business processes it supports Which records it creates or maintains Who will use it What decisions depend on its outputs Whether failure could affect product quality Whether failure could affect patient safety Whether failure could compromise data integrity Which regulatory requirements apply A system cannot be meaningfully assessed without a clear intended use. Testing every available feature is usually inefficient, while testing too little creates uncontrolled risk.
The appropriate scope should reflect how the organization will actually configure and use the software.
Risk-Based Classification of Software Functions CSA encourages teams to assess risk at the function or feature level rather than assigning one level of rigor to the entire system.
For example, a quality management platform may contain:
A function that approves a critical quality decision A function that calculates a regulated result A dashboard that displays previously approved information A notification setting A visual preference option These functions do not necessarily create the same level of risk.
A practical assessment may consider:
What happens if the function fails? Could the failure affect patient safety? Could it affect product quality? Could it compromise data integrity? Would another control detect the failure? How likely is the failure to remain undetected? What level of evidence is needed to establish confidence? Functions with higher potential impact should receive more rigorous assurance. Lower-risk features may be evaluated through lighter testing, supplier evidence, or unscripted methods.
Scripted and Unscripted Testing One of the most important CSA concepts is selecting a testing method that matches the risk and the nature of the function.
Scripted Testing Scripted testing defines test steps, expected results, and acceptance criteria before execution.
It may be appropriate for:
High-risk calculations Critical workflows Electronic signatures Security controls Data transfers Functions affecting product disposition Automated decision logic Regulatory record controls Scripted testing provides repeatability and clear objective evidence, but excessive scripting can make testers focus on following instructions rather than identifying unexpected behavior.
Unscripted Testing Unscripted testing gives the tester greater freedom to investigate how the software behaves.
Examples include:
Exploratory testing Error guessing Scenario testing Ad hoc testing Boundary testing Unscripted testing does not mean uncontrolled or undocumented testing. The organization should still record the objective, tester, date, results, issues identified, and conclusion.
It can be especially effective when knowledgeable users need to evaluate usability, configuration, workflows, or lower-risk functions.
What Counts as Sufficient Objective Evidence? CSA focuses on retaining enough evidence to demonstrate that the software was assessed and performed as intended.
Evidence may include:
Test records generated by a digital platform Automated test logs System reports Audit trail entries Exception records Configuration records Electronic approvals Screenshots where they provide meaningful evidence Supplier test results Exploratory testing notes Defect and deviation records Traceability between risks, requirements, and tests The amount of evidence should depend on risk. Capturing a screenshot for every click may produce a large validation package without adding meaningful assurance.
Evidence should show what was tested, who performed the activity, what happened, whether the result was acceptable, and how any problem was resolved.
Common Misunderstandings About CSA “CSA Means Less Testing” CSA does not necessarily require less testing. It requires testing effort to be directed toward functions that matter most.
A high-risk function may receive more rigorous testing under CSA than it did under a document-driven CSV process.
“CSA Eliminates Documentation” CSA aims to eliminate unnecessary documentation, not all documentation. Organizations still need sufficient records to demonstrate their reasoning, assurance activities, results, and conclusions.
“Unscripted Testing Requires No Evidence” Exploratory or unscripted testing should still produce an attributable and reviewable record.
“CSA Applies Automatically to Every GxP System” The regulatory scope, system type, intended use, and applicable requirements must be evaluated. FDA’s CSA guidance specifically addresses software used in medical device production and quality management systems.
“Supplier Testing Removes the Customer’s Responsibility” Supplier evidence can reduce duplicated effort, but the regulated organization remains responsible for its intended use, configuration, procedures, user access, integrations, and GxP decisions.
Benefits of a Risk-Based CSA Approach When appropriately implemented, CSA can help organizations:
Focus resources on critical functions Reduce low-value documentation Improve tester engagement Identify defects more effectively Make greater use of automation Respond faster to software releases Use supplier evidence more intelligently Strengthen risk-based decision-making Maintain validation more efficiently Support innovation without reducing control The objective is not simply to reduce costs or accelerate implementation. The central objective is to establish confidence in software while using resources proportionately.
How Digital Platforms Support CSV and CSA Digital validation and quality platforms can help connect intended use, requirements, risks, tests, results, deviations, changes, and approvals.
Examples within the life sciences software landscape include:
Validfor provides an AI-native digital validation platform supporting validation lifecycle, test, change, deviation, traceability, and periodic review activities. Its test management capabilities accommodate different assurance and testing methods within structured GxP workflows.
Kneat supports digital validation across computerized systems, equipment, facilities, analytical instruments, and commissioning and qualification processes.
ValGenesis provides validation and process lifecycle management solutions, including risk-based CSV, CQV, cleaning validation, and continuous process verification.
Veeva offers cloud applications across life sciences. Veeva Quality Cloud supports quality documents, QMS processes, training, and laboratory quality operations.
MasterControl provides connected quality and manufacturing solutions for regulated companies, including document control, training, quality events, manufacturing records, and GxP workflows.
These platforms have different functional scopes. Selecting a system should begin with intended use and process requirements rather than assuming that every digital quality or validation solution serves the same purpose.
How to Transition From Document-Heavy CSV to CSA
- Review Existing Validation Procedures Organizations should identify requirements that create documentation without meaningfully increasing assurance.
Procedures may need to be revised to permit risk-based testing, unscripted methods, supplier evidence, and automated test results.
-
Define a Risk Framework Teams need clear criteria for distinguishing higher-risk and lower-risk functions. Without an agreed framework, different projects may make inconsistent decisions.
-
Start With a Pilot System A controlled pilot allows the organization to test its methodology, templates, evidence requirements, and approval process before wider adoption.
-
Train Quality and Business Teams CSA depends on critical thinking. Training should therefore cover intended use, functional risk, testing methods, evidence expectations, and decision-making—not just new templates.
-
Use Supplier Evidence Strategically Supplier assessments and available documentation should be reviewed to determine what evidence is reliable and reusable.
-
Modernize Test Records Digital test execution, automated logs, electronic approvals, and connected traceability can reduce the manual work associated with maintaining test evidence.
-
Measure the Outcome Useful indicators may include:
Validation cycle time Review time Number of duplicated tests Defects detected Deviations caused by documentation errors Time spent producing evidence Change implementation time Percentage of automated tests Time required to prepare for an audit Metrics should confirm that efficiency improvements do not reduce software quality or regulatory control.
CSA for Cloud and SaaS Systems Cloud and SaaS applications may receive frequent updates, making repeated document-heavy validation difficult to sustain.
A CSA-oriented approach can help organizations:
Assess release impact Identify affected functions Review supplier release evidence Reuse existing test assets Apply regression testing according to risk Automate repeatable tests Document decisions efficiently Maintain traceability between changes and assurance activities Not every software release requires complete revalidation. A documented impact assessment should determine whether the change affects intended use, configuration, critical functions, interfaces, data integrity controls, or regulated records.
Conclusion The CSV vs. CSA discussion should not be reduced to “old validation versus new validation.” Both approaches aim to establish confidence that computerized systems perform reliably and remain suitable for their intended use.
CSA strengthens this objective by emphasizing critical thinking, functional risk, appropriate testing methods, and sufficient objective evidence. It can help life sciences organizations move away from document volume as a measure of quality and focus instead on meaningful assurance.
A successful transition requires updated procedures, trained personnel, clear risk criteria, suitable digital tools, and strong quality oversight. When implemented correctly, CSA can make software assurance more efficient without weakening patient safety, product quality, data integrity, or regulatory accountability.
Frequently Asked Questions What is the main difference between CSV and CSA? Traditional CSV often emphasizes formal documentation and predefined testing, while CSA emphasizes critical thinking, functional risk, appropriate assurance methods, and sufficient objective evidence.
Does CSA eliminate the need for validation? No. Organizations must still demonstrate that computerized systems are fit for their intended use. CSA provides a risk-based way to establish and document that confidence.
Does CSA apply to pharmaceutical companies? The FDA guidance formally focuses on software used in medical device production and quality management systems. Pharmaceutical organizations may adopt similar risk-based principles, but they must evaluate their own regulatory requirements and quality systems.
Can exploratory testing be used in a regulated environment? Yes, when appropriate for the function and risk. The purpose, tester, execution, observations, results, issues, and conclusion should still be documented.
Is scripted testing still necessary under CSA? Yes. Scripted testing remains appropriate for many higher-risk functions, critical calculations, security controls, electronic signatures, interfaces, and automated decisions.
Can digital validation software support both CSV and CSA? Yes. A suitable platform can support lifecycle documentation, risk assessments, scripted and unscripted testing, objective evidence, deviations, approvals, and traceability.